
Amazon has revealed that its threat intelligence team recently disrupted a sophisticated—or, as described, opportunistic—watering‑hole campaign orchestrated by the Russian state‑sponsored hacking group APT29. Also known by various aliases including Cozy Bear, Midnight Blizzard, BlueBravo, Earth Koshchei, and The Dukes, APT29 operates under the SVR, Russia’s Foreign Intelligence Service.
How the Attack Unfolded
Amazon identified a campaign in which legitimate websites were compromised to inject malicious JavaScript. About 10% of site visitors were redirected to attacker-controlled domains—such as findcloudflare[.]com—which were designed to mimic Cloudflare verification pages.
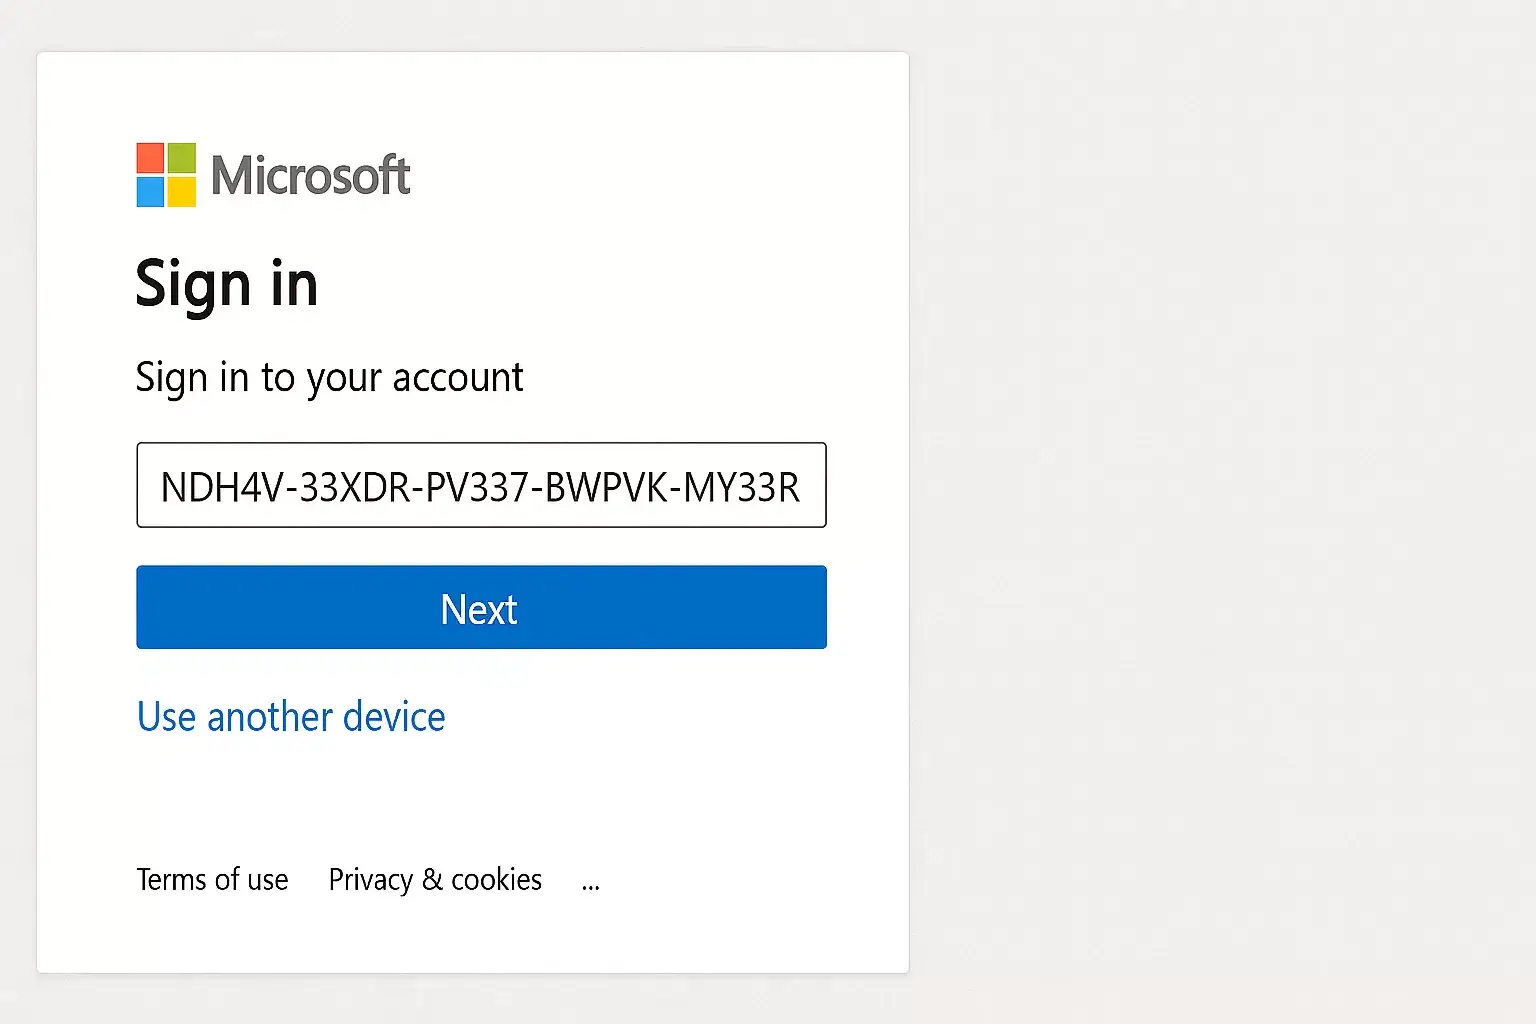
Once diverted, visitors encountered a sign-in workflow where they were tricked into entering a device code that in fact originated from the attackers. By doing so, users inadvertently authorized rogue devices, granting APT29 access to their Microsoft accounts and the associated data.
Evasive Tactics and Innovation
The sophistication of the campaign lay not only in its deceptive façade but also in its stealth tactics:
- Base64 encoding was used to conceal malicious code from detection.
- Randomized redirection, affecting only a small subset (≈10%) of visitors per site, minimized exposure and detection risk.
- Cookie‑based suppression, which prevented the same visitor from being redirected multiple times.
- Infrastructure pivoting, where APT29 moved operations off AWS to new cloud providers when blocked.
After Amazon’s initial disruption, the attackers attempted to shift execution by registering domains like cloudflare.redirectpartners[.]com, again targeting users via device code workflows.
A History of Escalation
This operation follows earlier campaigns in APT29’s evolving playbook. In October 2024, Amazon interrupted attempts by the group to use phishing domains impersonating AWS to deliver malicious RDP files.
Moreover, in June 2025, Google’s Threat Intelligence Group reported APT29-linked campaigns abusing Google’s application‑specific passwords feature to access victims’ emails, under the cluster UNC6293.
All these efforts illustrate APT29’s broader strategy: improving technical sophistication, scaling operations, and expanding their net through diversified phishing strategies—from device code and device‑join phishing to abusing cloud‑based authentication flows.
Amazon’s Response and Collaborative Defense
Amazon’s security team took immediate action: isolating compromised EC2 instances, coordinating with Cloudflare and other service providers to dismantle malicious infrastructure, and sharing key intelligence with Microsoft to limit the campaign’s reach. Importantly, Amazon stated that no AWS systems were compromised, and there was no direct impact on AWS services.
Despite APT29’s pivot off AWS infrastructure, Amazon’s continuous monitoring allowed them to track and disrupt the adversary’s shifting operations—typified by the emergence of new spoofing domains referencing Cloudflare.
Citing CJ Moses, Amazon’s Chief Information Security Officer, the company emphasized:
“This opportunistic approach illustrates APT29’s continued evolution in scaling their operations to cast a wider net in their intelligence collection efforts.”
What It Means Going Forward
The incident serves as both a warning and a case study in cybersecurity vigilance. By exploiting trusted authentication flows—such as Microsoft’s device code mechanism—state-sponsored actors like APT29 increasingly blur the boundaries between legitimate system behavior and malign manipulation.
Organizations must stay alert to these tactics by:
- Monitoring unusual authentication events, especially around device code issuance and validation.
- Employing red-team simulations to test user resistance to deceptive authentication workflows.
- Collaborating across security communities—corporate, cloud providers, and platform owners—to rapidly detect and disrupt advanced threats.
For APT29, this watering-hole method represents yet another nail in their evolving arsenal, combining deception, technology exploitation, and infrastructure agility. For defenders, it’s a reminder that maintaining trust in existing systems requires constant adaptation, cross-platform awareness, and proactive threat intelligence.
Please subscribe to the Newsletter so that you do not miss any critical update