
Critical Commvault Vulnerability Actively Exploited, Added to CISA’s KEV Catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical vulnerability affecting Commvault’s Command Center to its Known…
SentinelOne Uncovers Chinese APT ‘PurpleHaze’ Targeting Global Enterprises in Espionage Campaign
Cybersecurity firm SentinelOne has identified a sophisticated cyber-espionage campaign attributed to a China-linked threat cluster known as “PurpleHaze.” This group…
Over 1,200 SAP NetWeaver Servers Exposed to Critical Vulnerability Actively Exploited in the Wild
A critical security flaw in SAP NetWeaver Application Server has left over 1,200 servers exposed to potential attacks, with threat…
Supply Chain Cyberattack Hits South Korean Firms: Lazarus Group Behind Operation
In a recent surge of cyber activity attributed to North Korea’s notorious Lazarus Group, six South Korean firms across various…
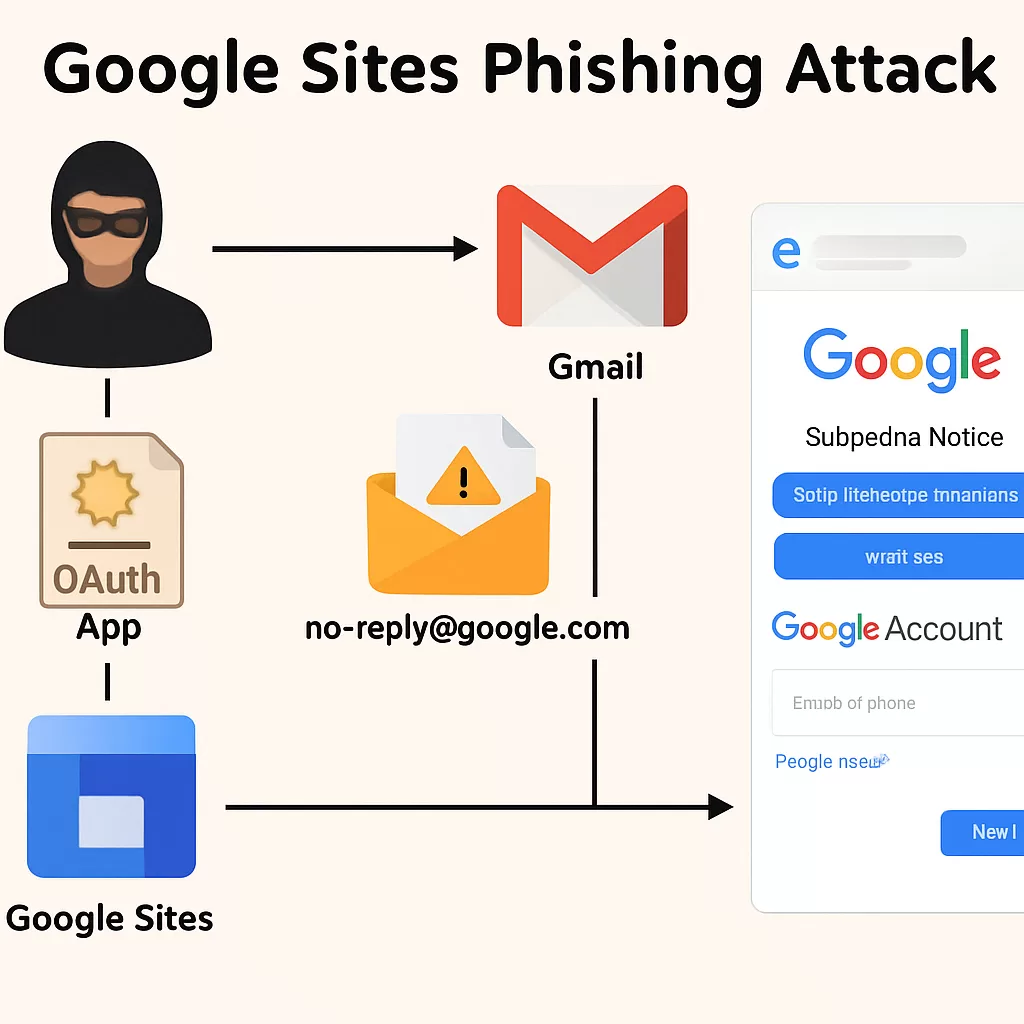
Phishers Exploit Google Sites and DKIM Protections to Launch Sophisticated Attacks
In a concerning development, cybercriminals are exploiting trusted Google services—particularly Google Sites and DomainKeys Identified Mail (DKIM)—to bypass traditional security…
Chinese Hackers Deploy Upgraded MysterySnail RAT to Target Russian and Mongolian Governments
A suspected Chinese state-sponsored hacking group, known as IronHusky, has launched a sophisticated cyber-espionage campaign targeting Russian and Mongolian government…
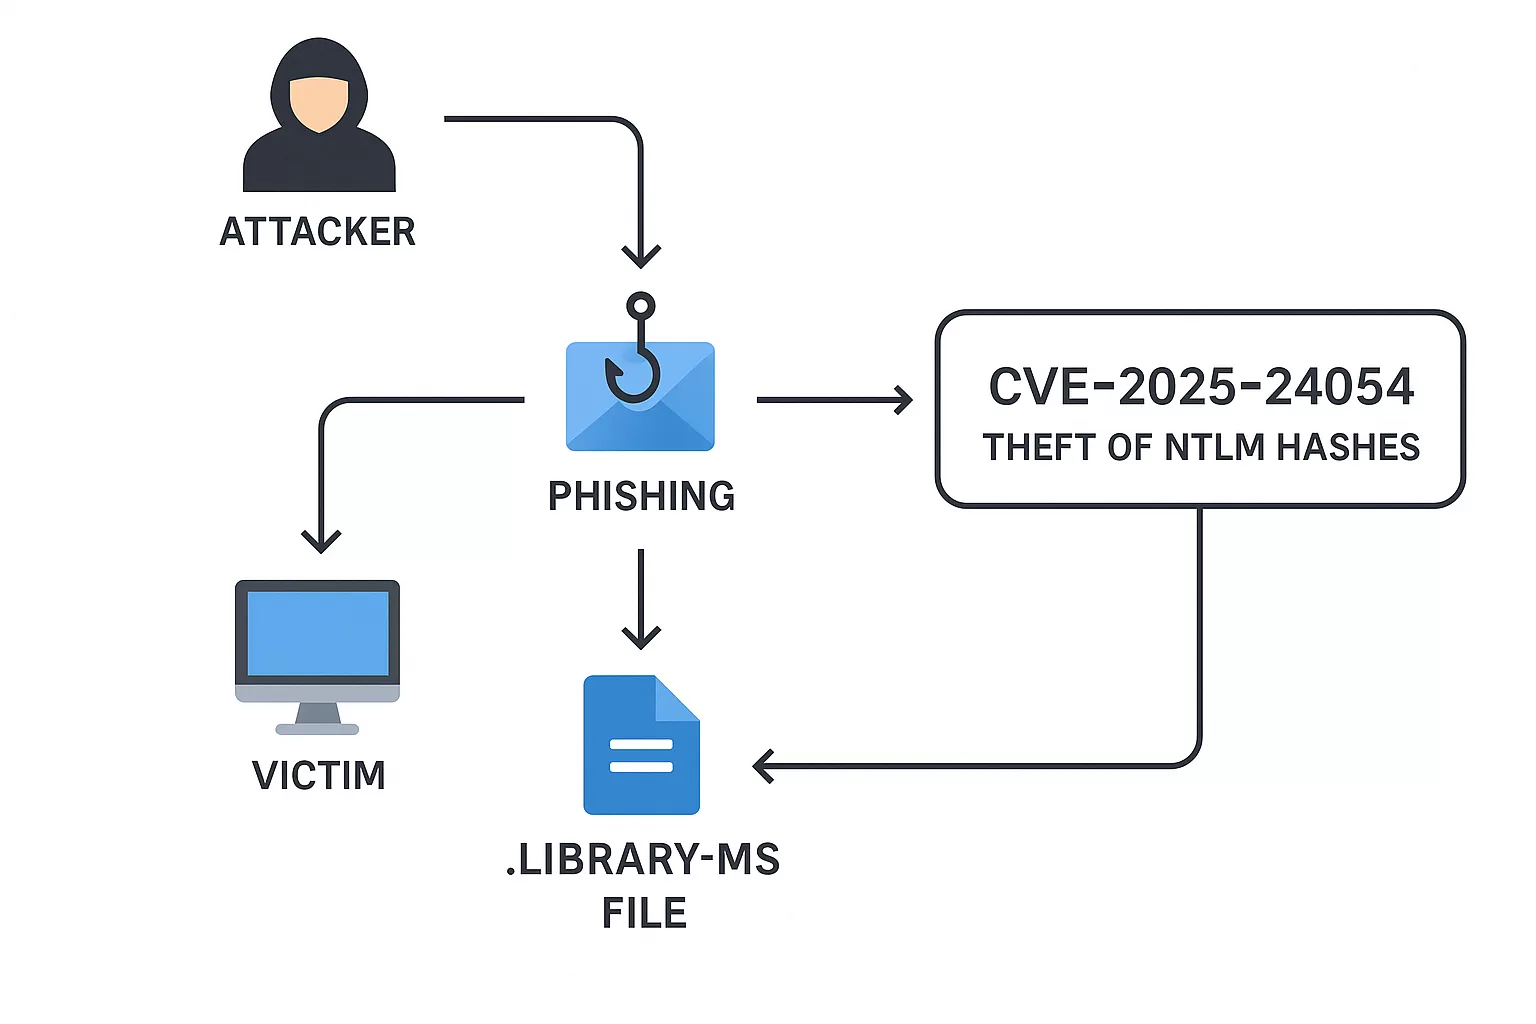
Windows Vulnerability CVE-2025-24054 Actively Exploited to Steal NTLM Credentials
A medium-severity vulnerability in Microsoft Windows, identified as CVE-2025-24054, is currently under active exploitation, enabling attackers to steal NTLM credentials…
U.S. Government Extends Funding for MITRE’s CVE Program Amid Cybersecurity Concerns
In a critical move to maintain global cybersecurity infrastructure, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) has extended its…
Pakistan-Linked Hackers Expand Espionage Campaigns, Targeting Key Indian Sectors with Advanced Malware
A Pakistan-linked cyber espionage group has significantly broadened its targeting footprint in a new wave of attacks against Indian organizations.…
SpyNote, BadBazaar, and MOONSHINE Malware Exploit Fake Apps to Target Android and iOS Users
Cybersecurity experts have uncovered a series of sophisticated malware campaigns—SpyNote, BadBazaar, and MOONSHINE—designed to compromise Android and iOS devices through…